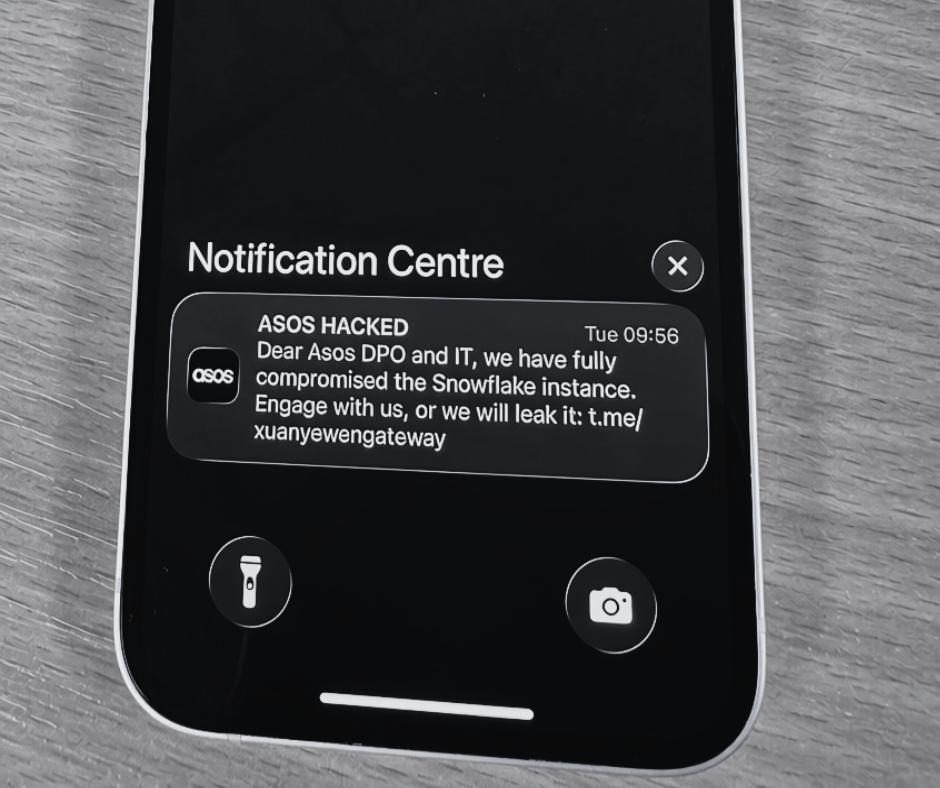
Earlier this week, ASOS customers were met with an unexpected push notification appearing to come from the retailer’s own app.
The message claimed that ASOS had been hacked and threatened to leak information unless the attackers were engaged with.
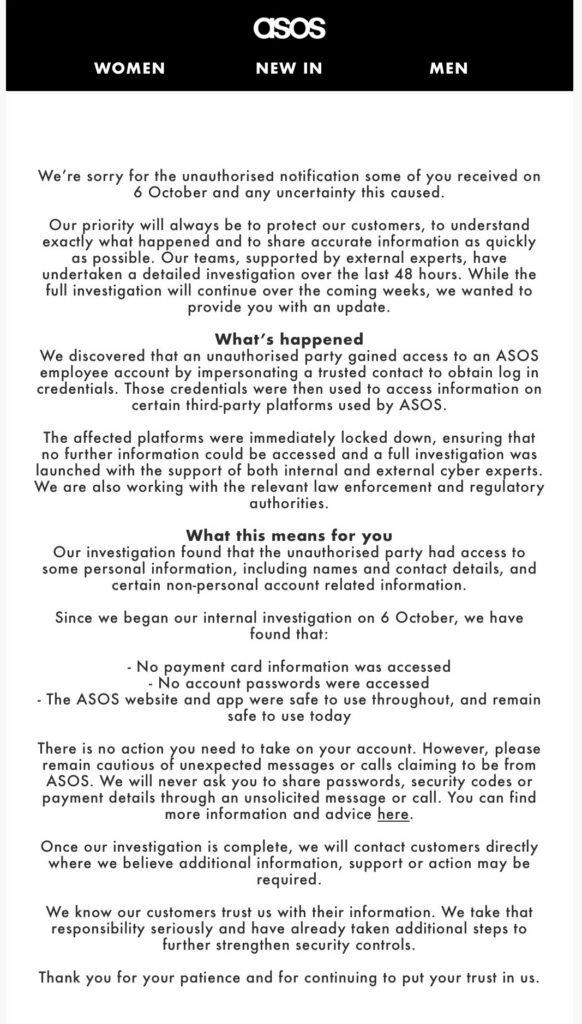
ASOS has since confirmed that an unauthorised party gained access to an employee account by impersonating a trusted contact to obtain login credentials. Those credentials were then used to access information held on certain third-party platforms used by ASOS.
While ASOS has stated that its website and app remain operational, the incident highlights an important lesson that cyber security isn’t just an IT responsibility. Every employee plays a role in protecting a business.
How did the ASOS attack happen?
According to ASOS’s latest update, the attacker gained access to an employee account after impersonating a trusted contact and obtaining their login credentials. Those credentials then provided access to third-party platforms used by the company.
Sometimes, the weakest point in a security system can simply be a convincing message, phone call, or email.
An attacker may pretend to be:
- A colleague or manager
- A supplier
- A customer
- An IT support provider
- A trusted third party
- A senior member of the organisation
They may then create a sense of urgency, authority or familiarity to persuade someone to provide information or credentials.
This is why technical security measures need to be supported by well-trained employees.
The Importance of Employee Cyber Security Awareness
Businesses can invest heavily in firewalls, endpoint protection, backups, monitoring and other technical security measures, but if an employee is successfully persuaded to hand over their credentials, an attacker may be able to bypass some of those defences by using a legitimate account.
Regular cyber security awareness training can help employees recognise the warning signs of an attempted attack and understand what they should do when something doesn’t look right.
Employees should be able to flag:
- Unexpected requests for login credentials
- Urgent requests from senior colleagues
- Unusual requests from suppliers or customers
- Emails asking them to click unfamiliar links
- Unexpected password or account requests
- Messages that create pressure or urgency
The Reputational Impact of a Cyber Attack
The consequences of a cyber incident aren’t just stolen data or system downtime; there can also be a significant impact on customer trust and reputation.
ASOS moved quickly to restrict access to the affected notification platforms and confirmed that its website and app continued to operate normally. It also stated that basic personal information, including names and contact details, may have been accessed, while payment-card information and account passwords were not believed to have been affected.
Even if critical systems remain operational, a cyber incident can create uncertainty for customers.
Therefore it’s important to think about cyber security from more than just a technical perspective.
What can you Learn from the ASOS Attack?
There are several lessons SMEs can take from this incident.
1. Train your employees
Employees should receive regular guidance on phishing, social engineering, impersonation attacks, password security and how to report suspicious activity.
2. Encourage employees to question unusual requests
Employees should know they can reach out if they receive an unexpected or unusal message. Even if it’s a false alarm, it’s better to be safe than sorry.
3. Use multi-factor authentication
Multi-factor authentication adds another layer of protection and can make it considerably harder for an attacker to access an account using stolen credentials.
4. Review third-party platforms
Understand what third-party platforms you use, what information they hold and what access they have to your wider environment.
5. Limit access
Employees should only have access to the systems and information they need to perform their role.
If an account is compromised, limiting its permissions can help reduce the potential impact.
Cyber Security is Everyone’s Responsibility
The ASOS incident is an important reminder during Cyber Security Awareness Month that cyber security is not just the IT department’s role.
Your IT team can put the technology and security controls in place, but your employees are often the people receiving the emails, answering the phone calls and responding to messages that could be used by cyber criminals.
Giving them the knowledge to be able to recognise a threat is very important.
If the ASOS incident has made you question your own business’s cyber security, now is a good time to review your current defences, employee awareness and approach to protecting your data.
At Immervox, we help businesses understand where their cyber security could be improved and put practical measures in place to help keep their people, systems and data protected.
Want to understand how secure your business really is? Get in touch with us to discuss your cyber security.